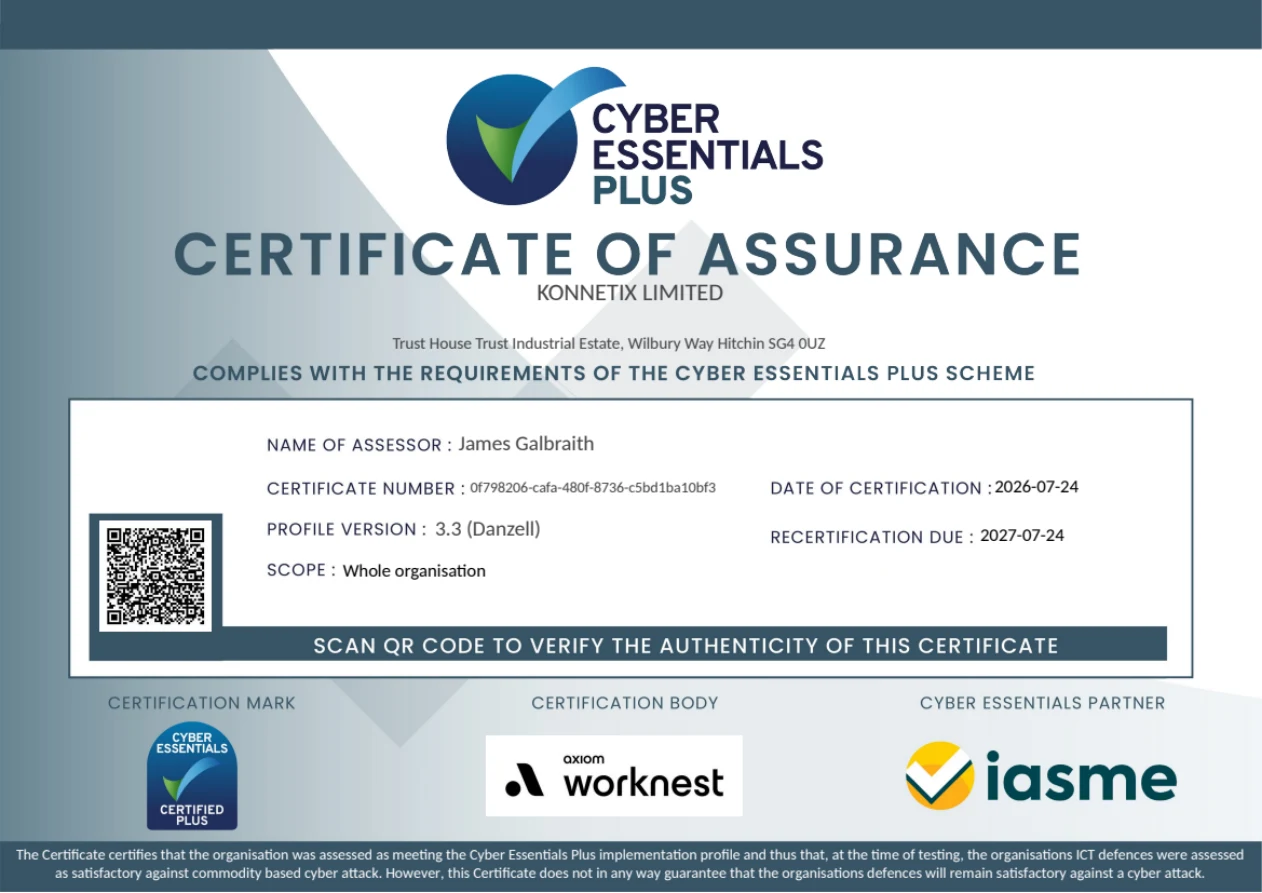
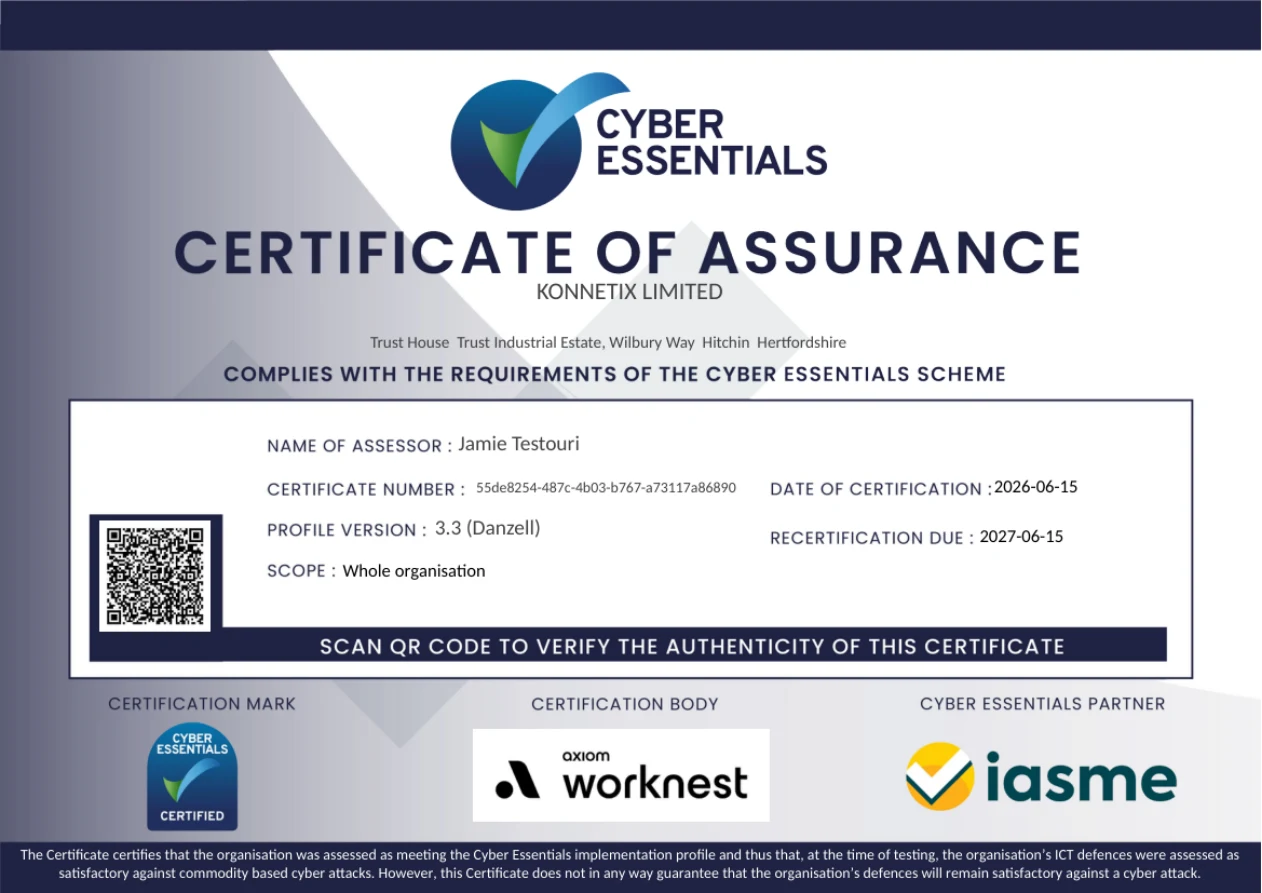
Konnetix Limited holds both Cyber Essentials Plus and Cyber Essentials, covering the whole organisation. Here are the certificates themselves, so you can read the scope and dates for yourself.
Select a certificate to open the original PDF in a new tab.
Cyber Essentials Plus
Includes the Cyber Essentials self-assessment plus independent technical testing of devices and systems.
Certified organisation
Konnetix Limited
Scope
Whole organisation
Certified
24th July 2026
Recertification due
24th July 2027
Certificate number
0f798206-cafa-480f-8736-c5bd1ba10bf3
Certification body
axiom worknest, partner of IASME
Cyber Essentials
A self-assessment of baseline technical controls, reviewed by the certification body.
Certified organisation
Konnetix Limited
Scope
Whole organisation
Certified
15th June 2026
Recertification due
15th June 2027
Certificate number
55de8254-487c-4b03-b767-a73117a86890
Certification body
axiom worknest, partner of IASME
What Our Cyber Essentials Certifications Demonstrate
Achieving certification means meeting defined technical requirements, not simply buying a security product or displaying a badge. Our certificates cover the whole organisation and record assessment against version 3.3 (Danzell), the current Cyber Essentials requirements introduced in April 2026.
We take that responsibility seriously. Our approach is to maintain the controls that protect our business, not just prepare for an assessment. As your IT partner, we believe the standards we help you work towards should matter within our own organisation too.
Five Technical Control Areas
Firewalls
Correctly configured protection for in-scope devices and networks, with unnecessary incoming connections blocked and permitted access controlled.
Secure Configuration
Secure device and system settings, including removing unnecessary accounts and software, changing default passwords and protecting access to devices.
Security Update Management
Supported software and timely vulnerability fixes. Qualifying high-risk or critical security updates must be applied within 14 days of release, with further criteria set out in the requirements.
User Access Control
Approved user accounts, access limited to what each role needs, separate administrative accounts and removal of access when it is no longer required. Cloud services must use multi-factor authentication where it is available.
Malware Protection
Active, maintained protection to prevent malicious software from running, using appropriately configured anti-malware or application allow listing as required for the devices in scope.
Verified Assessment, with Additional Testing for CE+
Cyber Essentials
A verified self-assessment reviewed by a certification body against the scheme's requirements. A director or board member signs a declaration acknowledging responsibility for maintaining compliance throughout the certification period.
Cyber Essentials Plus
Adds an independent technical audit to test that the controls are working in practice, using a sample of the in-scope environment. It provides additional assurance beyond the verified self-assessment, rather than relying on written answers alone.
Clear Requirements for Modern, Cloud-Based Businesses
Under the April 2026 requirements, cloud services holding organisational data or services cannot simply be excluded from scope. MFA must be used for cloud services wherever it is available, including when it is a paid option. Failure to meet the specified MFA or high-risk update requirements results in an assessment failure.
The CE+ process also strengthens checks on update management: where an initial sample fails, remediation and retesting include a new random sample as well as the original devices. Updating only the devices selected for testing is not enough.
For customers choosing an IT provider, our certification offers independently assessed evidence of how seriously we take these technical controls within our own business. We bring the same commitment to helping customers understand their requirements and address the work needed for their own certification.
Certification records the assessment at the date of issue and supports, rather than replaces, ongoing security management; no certification guarantees protection against every attack.